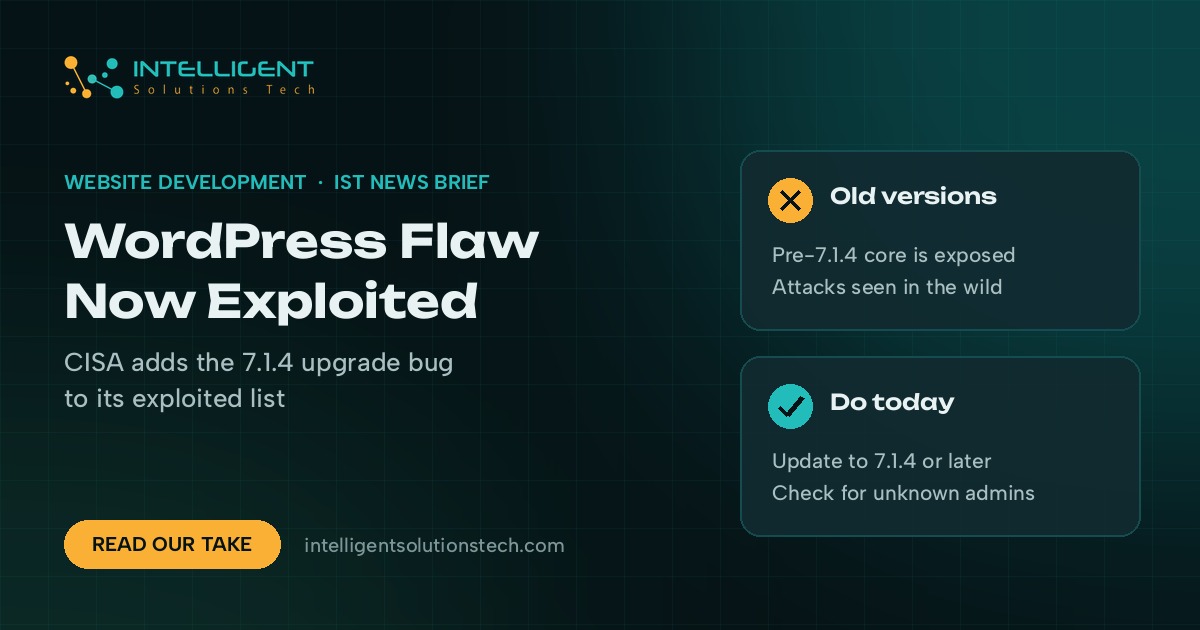
The US Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-119977, a WordPress core vulnerability, to its Known Exploited Vulnerabilities catalog on November 3, 2026. That means attackers are using it against real sites now. WordPress fixed the bug on October 28 in version 7.1.4, which we covered when it shipped. Any site that still hasn’t updated is the target.
What’s new
CISA’s catalog entry describes a time-of-check time-of-use race condition in the WordPress core upgrader. During a full-package core upgrade, WordPress uses staging paths that are predictable and reachable from the web, and an unauthenticated attacker can use that window to run code on the server. The WordPress security team called it a weakness that can lead to remote code execution during the upgrade window.
CISA gave US federal agencies until November 6 to fix it and marked the entry for forensic triage, so agencies are expected to check for signs of a break-in as well as patch. BleepingComputer reported that Wordfence blocked more than 13,000 attacks aimed at this flaw in a single day.
Who it affects
Every self-hosted WordPress site that hasn’t installed 7.1.4 or the matching security release for its branch. Sites with automatic background updates switched on should already have it. The ones we worry about are sites where auto-updates were turned off years ago, staging copies left online, and sites whose host pins an older version.
Shopify, Squarespace and Wix stores aren’t affected. Managed WordPress hosts usually push core security releases quickly, but it’s still worth checking.
Our take
We’d handle this today rather than leave it for the weekend. Two steps cover most sites:
- Open Dashboard, then Updates, and confirm the site reports WordPress 7.1.4 or later. If it doesn’t, take a backup and update now.
- After updating, look for admin users you didn’t create, PHP files in the uploads folder and plugins nobody remembers installing. If you find any, rotate every admin password and hosting login before you clean up.
If you run several WordPress sites, check the forgotten ones first, since they’re the most likely to have missed the update. The primary sources are CISA’s KEV catalog and the WordPress 7.1.4 release notes. Our PHP2Shell brief covers the server-side checks in more detail.
Need someone to patch and check your sites? Our website maintenance team handles core updates, backups and post-update checks for WordPress sites.